


Smart cards, card readers and system requirements
Here you can check which smart cards and card readers are offered or supported by B-Trust, the certification validity of the cards, and their compatibility with different operating systems, browsers and software.
A qualified electronic signature must be created using a qualified electronic signature creation device (QSCD) that meets the requirements of Regulation (EU) No 910/2014, as amended by Regulation (EU) 2024/1183 of the European Parliament and of the Council.
When a smart card is used, the private key is created and stored in the protected environment of the card. Access to the private key is protected by a personal PIN. The smart card is connected to the computer through a card reader.
More than one electronic signature certificate may be stored on a smart card, provided that the certificate holder is the same person.
Smart card and card reader formats
You can choose between a standard-format or SIM-format smart card and card reader.
Standard format

SIM format
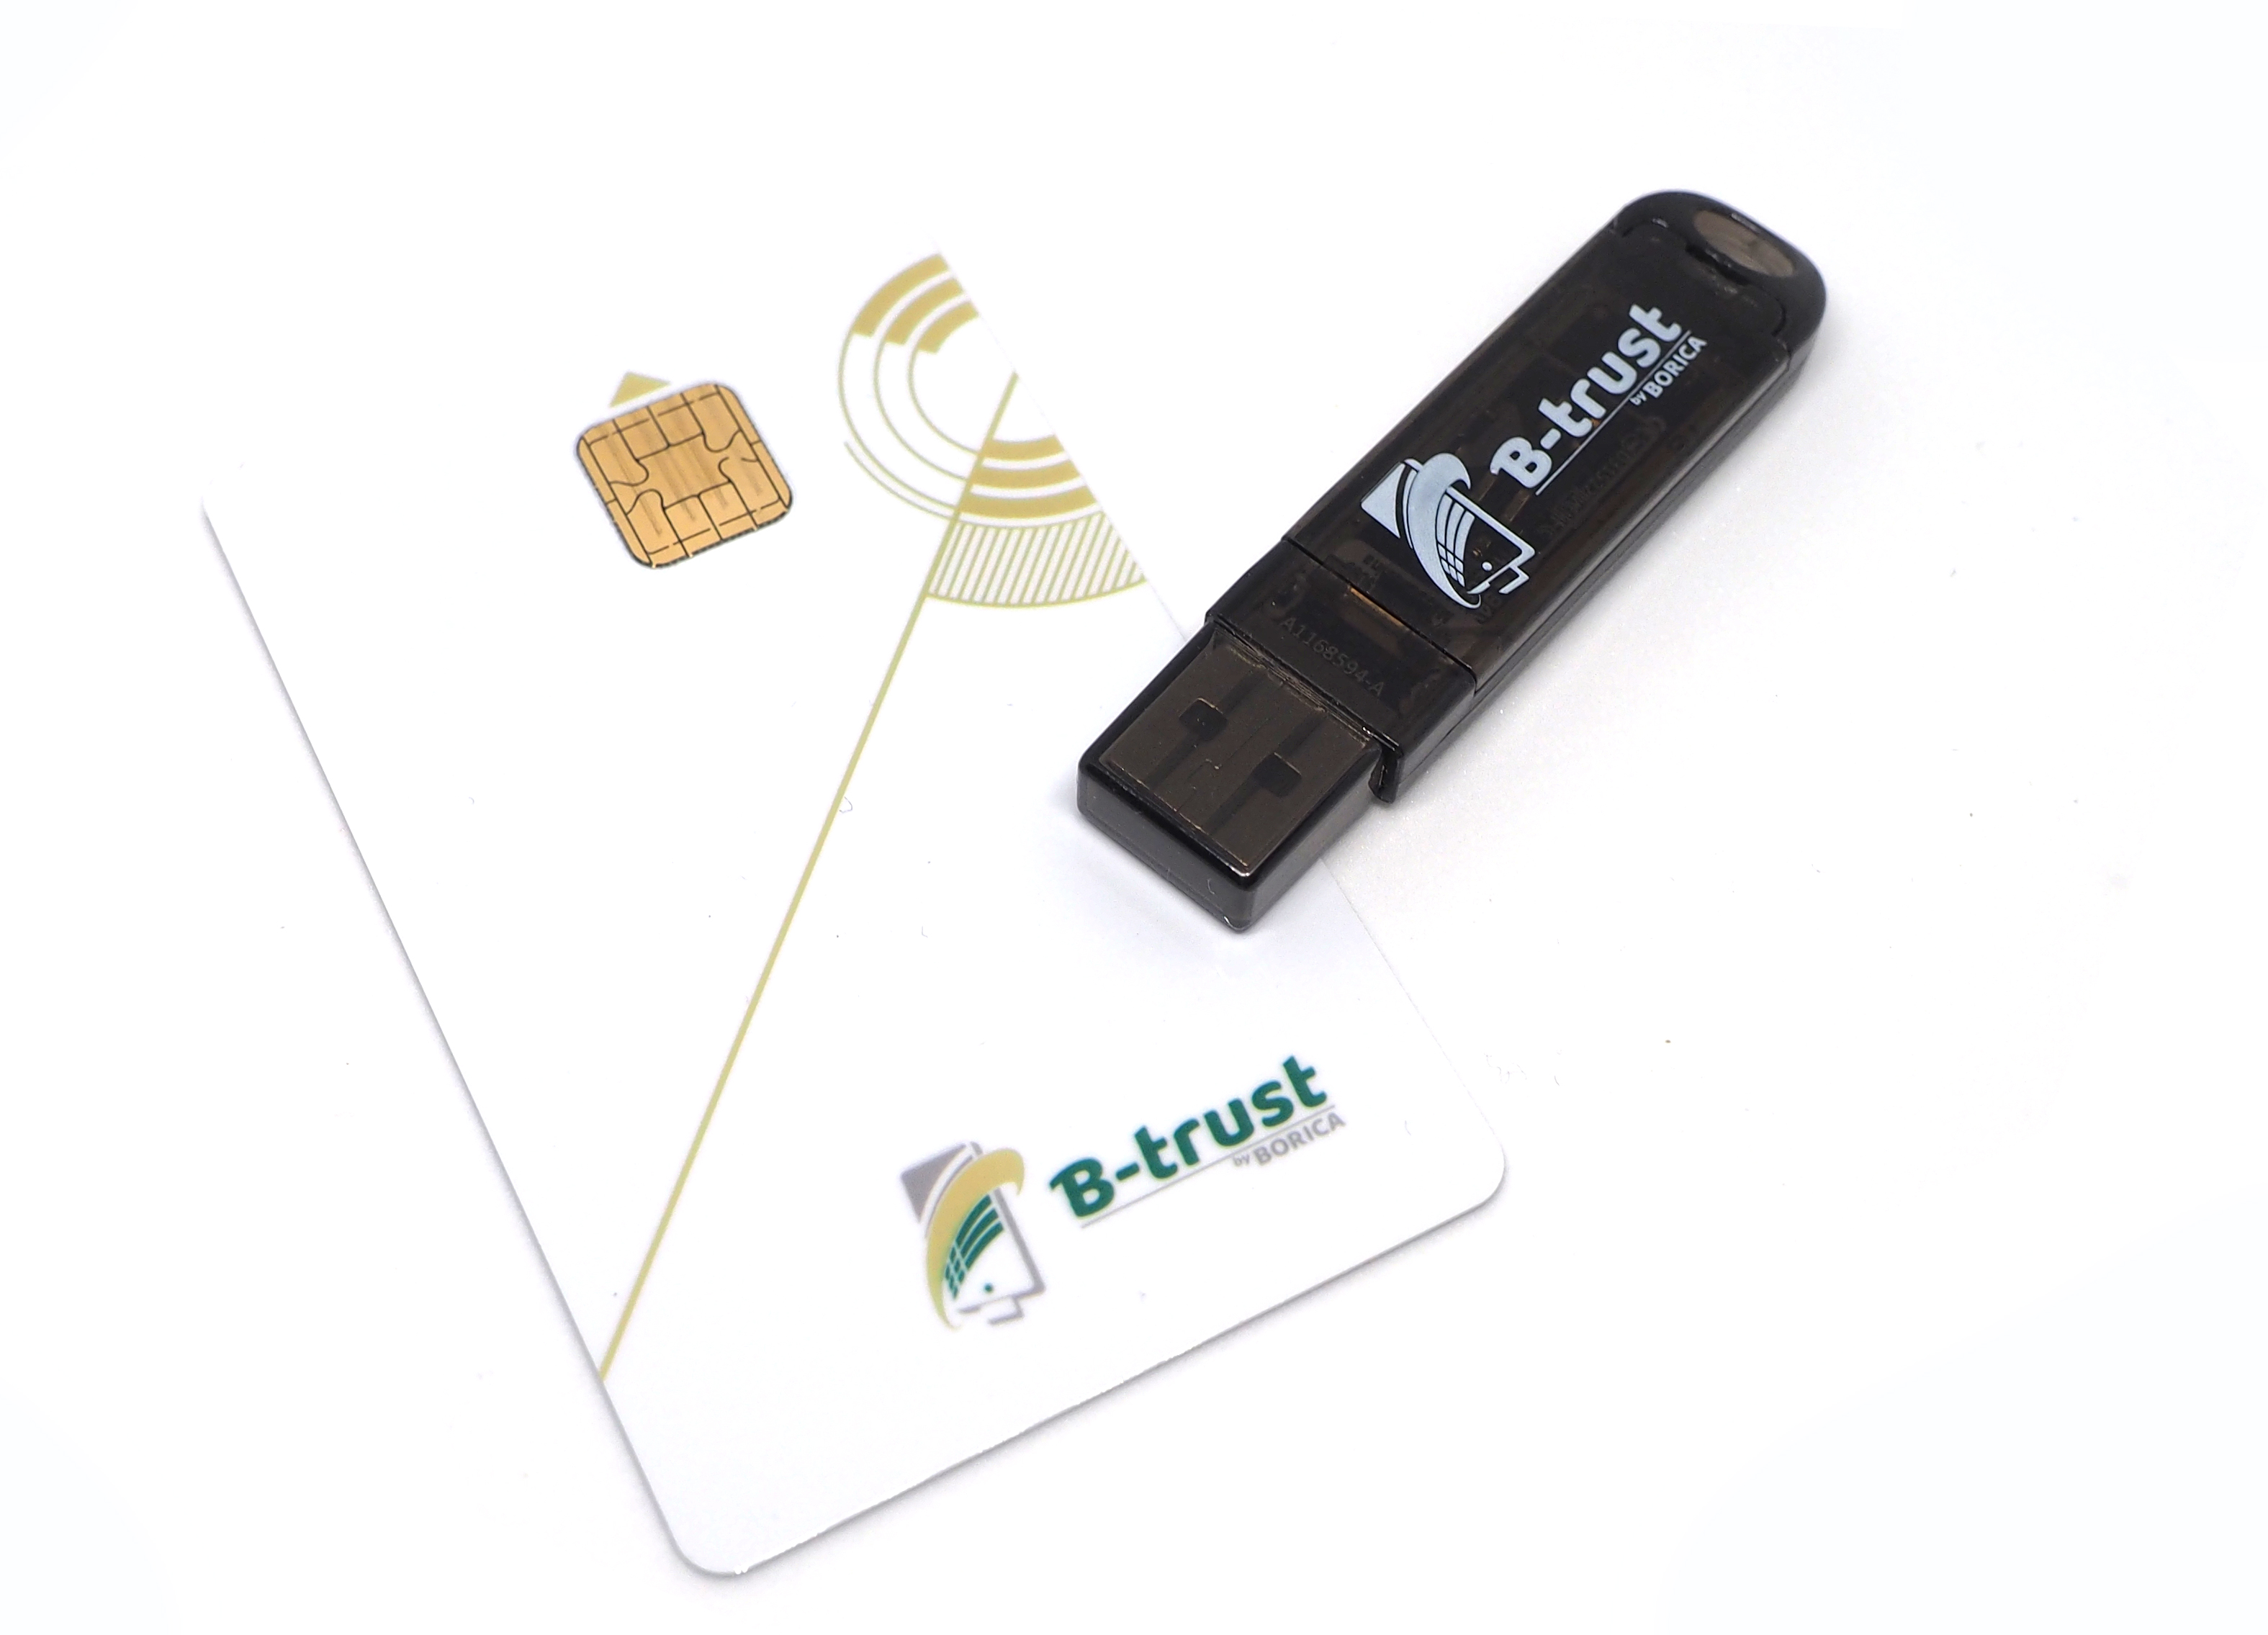
In the standard format, the smart card and card reader are separate. This format is suitable for use with a desktop computer in the office or at home.
In the SIM format, the smart card and card reader are combined in a compact device. This format is suitable for use with a laptop or at more than one workplace.
The models shown in the images are for illustration purposes only. BORICA AD reserves the right to change the models of smart cards and card readers offered without prior notice.
Smart cards
The table provides information about the smart cards offered or supported by B-Trust, as well as older models that must be replaced.
| Smart card | Status | Supported operations | Corresponding entry in the EC list | Certified until |
| Thales SafeNet IDPrime 940C SIM or standard format | Offered and supported | Issuance, reissuance and renewal of qualified certificates for electronic signatures | IAS Classic v5.2 on MultiApp v5.0 ANSSI-CC-2021/54 | 4 November 2031 |
| Thales SafeNet IDPrime 940B SIM or standard format | Supported but no longer offered | Issuance, reissuance and renewal of qualified certificates for electronic signatures on an existing smart card | IAS Classic v4.4.2 with MOC Server 1.1 on MultiApp v4.1 ANSSI-CC-2019/07 | 15 January 2029 |
| Gemalto IDPrime MD 940 SIM or standard format | Not supported | The card does not support the generation of 3072-bit RSA keys. Issuance, reissuance and renewal of qualified certificates for electronic signatures are not available. The card must be replaced. | IAS Classic v4.4.2 with MOC Server 1.1 on MultiApp v4.0.1 ANSSI-CC-2018/24 | 11 June 2028 |
| Gemalto IDPrime MD 840B SIM or standard format | Not supported | Issuance, reissuance and renewal of qualified certificates for electronic signatures are not available. The card must be replaced. | Application IAS V4 on MultiApp V3, component M7820 A11 ANSSI-CC-2014/50 | Expired |
| Gemalto IDPrime MD 840 SIM or standard format | Not supported | Issuance, reissuance and renewal of qualified certificates for electronic signatures are not available. The card must be replaced. | Application IAS V4 on MultiApp V3, component M7820 A11 ANSSI-CC-2014/50 | Expired |
| JCOP v2.4.1 | Not supported | Issuance, reissuance and renewal of qualified certificates for electronic signatures are not available. The card must be replaced. | Legacy model | Expired |
| Siemens CardOS v4.3B | Not supported | Issuance, reissuance and renewal of qualified certificates for electronic signatures are not available. The card must be replaced. | Legacy model | Expired |
The name shown in the European Commission list refers to the certified combination of hardware platform and application on which the respective smart card model is based.
The status “Not supported” may also apply to smart cards whose certification has not yet expired when their technical characteristics no longer meet the current requirements and policies of B-Trust, including requirements relating to cryptographic algorithms and key lengths.
The complete and up-to-date list of notified qualified and secure electronic signature and seal creation devices (QSCD/SSCD) is available on the European Commission website.
View the European Commission list
Smart card replacement
Smart cards have a limited lifecycle and must be replaced before their certification expires. After that date, the card cannot be used as a qualified electronic signature creation device for creating new qualified electronic signatures.
Replacement is also required when the technical characteristics of the card no longer meet the current requirements and policies of B-Trust, even if its certification has not yet expired.
When the card is replaced, a new certificate is issued and a new key pair is created on the new smart card. The expiry of the card certification or the replacement of the card does not invalidate qualified electronic signatures created with it beforehand.
The certification validity period is not a warranty period and does not indicate the technical condition of the card. It determines the period during which the device may be used as a QSCD under the applicable certification.
Card readers
The following card reader models are offered by B-Trust.
| Card reader | Format and connection | Manufacturer |
| CCR7115B-01 | SIM format, USB Type-A | Comitex |
| CCR7115B-02 | SIM format, USB Type-C | Comitex |
| Omnikey 1021 | Standard format, USB | HID Global |
| ACR 38 USB | Standard format, USB | Advanced Card Systems |
For the smart card to operate correctly, the card reader must be compatible with the card format, the operating system and the required software.
Supported operating systems and browsers
The table shows which combinations of operating system, internet browser and B-Trust smart card software are supported when using an electronic signature on a physical device.
| Operating system | Internet browser | Smart card software | ||
| Chromium-based browsers | Firefox | Cryptovision | Gemalto/SafeNet | |
| Windows 10, x32/x64 | ✔ | ✔ | ✔ | ✔ |
| Windows 11, x64 | ✔ | ✔ | ✔ | ✔ |
| Windows 11, ARM * | ✔ | ✔ | ✖ | ✔ |
| macOS versions 13, 14, 15 and 26 | ✔ | ✔ | ✖ | ✔ |
| Linux RHEL | ✔ | ✔ | ✖ | ✔ |
| Linux Ubuntu | ✔ | ✔ ** | ✖ | ✔ |
* Windows 11 ARM and Gemalto/SafeNet: On Windows devices with ARM processors, electronic signature operation depends on the installed Gemalto/SafeNet software. Installing the standard SafeNet Authentication Client for x86/x64 enables operation with software such as Adobe Acrobat Reader but disables browser functionality. Using the Gemalto/SafeNet software for ARM enables signing through browsers but not through Adobe Acrobat Reader.
** Linux Ubuntu and Firefox: The SNAP version of Mozilla Firefox does not allow the use of an electronic signature because of restrictions on access to system devices. Using an electronic signature requires Mozilla Firefox to be installed outside the SNAP environment.
Chromium-based browsers: Google Chrome, Microsoft Edge, Brave, Opera and other browsers based on Chromium.


